Axiom is a great destination for volumetric data sources for security use cases. We commonly see network traffic logs from firewalls, routers, switches, and wireless access points, and also endpoint telemetry logs like Sysmon, Sysdig, Falcon Data Replicator — they generate high volumes of data. In many cases customers make choices or play “event gymnastics” to move data between storage tiers, or archive data beyond 3-7 days, depending on their budget and the criticality or incident suspicions.
OPNsense is one of many popular open-source firewalls forked from the popular PFsense. It provides various event data through the syslog facility. The PF logs (filterlog) message field (Figure 1) is CSV text. The DNS logs that I chose from Unbound (Figure 2) are delimited with a space.
Figure 1 - PF Filterlog CSV IPv4/UDP Message Field
Figure 2 - Unbound DNS Server Message Field
One of the cool things with Axiom is that you can ship this data with fields or without. You can leave it up to query-time execution operated by lambdas to assign the fields later. I have an upcoming blog where I will share how I do this with a log shipper, but it’s purely preference. The amount of work is the same. Applied ahead of time it provides the benefit of simplified querying, or saving the query, values or both as virtual fields and relying on the query engine. Perhaps you have ingested event data that has been archived for compliance and retention purposes that you need to review for incident response or forensic purposes. This is a great way to extract that information and gain value without previously defining the logic in your log shipper or pipeline. I love the flexibility, since sometimes we get to delay the analysis until we need to do it — who doesn’t love procrastinating when your plate is full?
Here is what the query in Axiom’s APL looks like for messages similar to Figure 1, and for Figure 2:
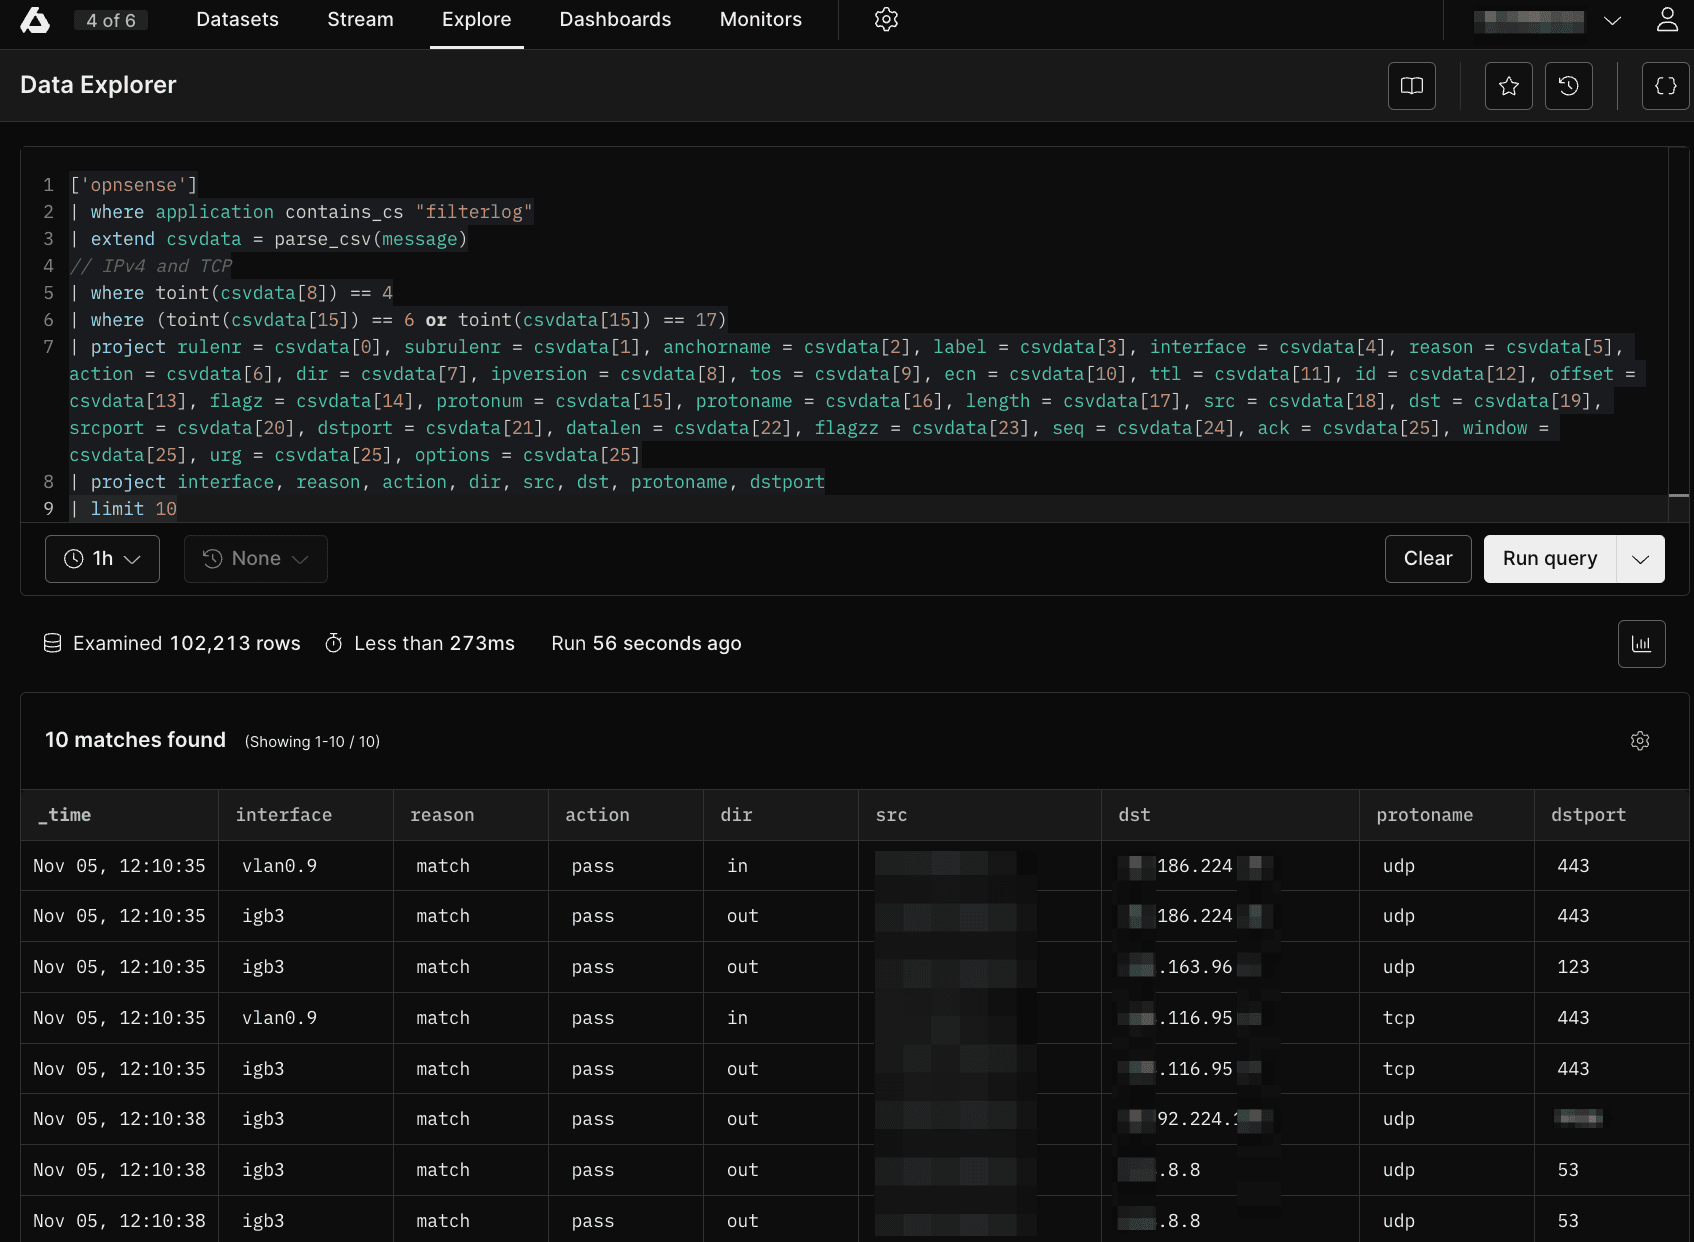
APL Parsing Filterlog IPv4 TCP/UDP Events
APL Query for the Above
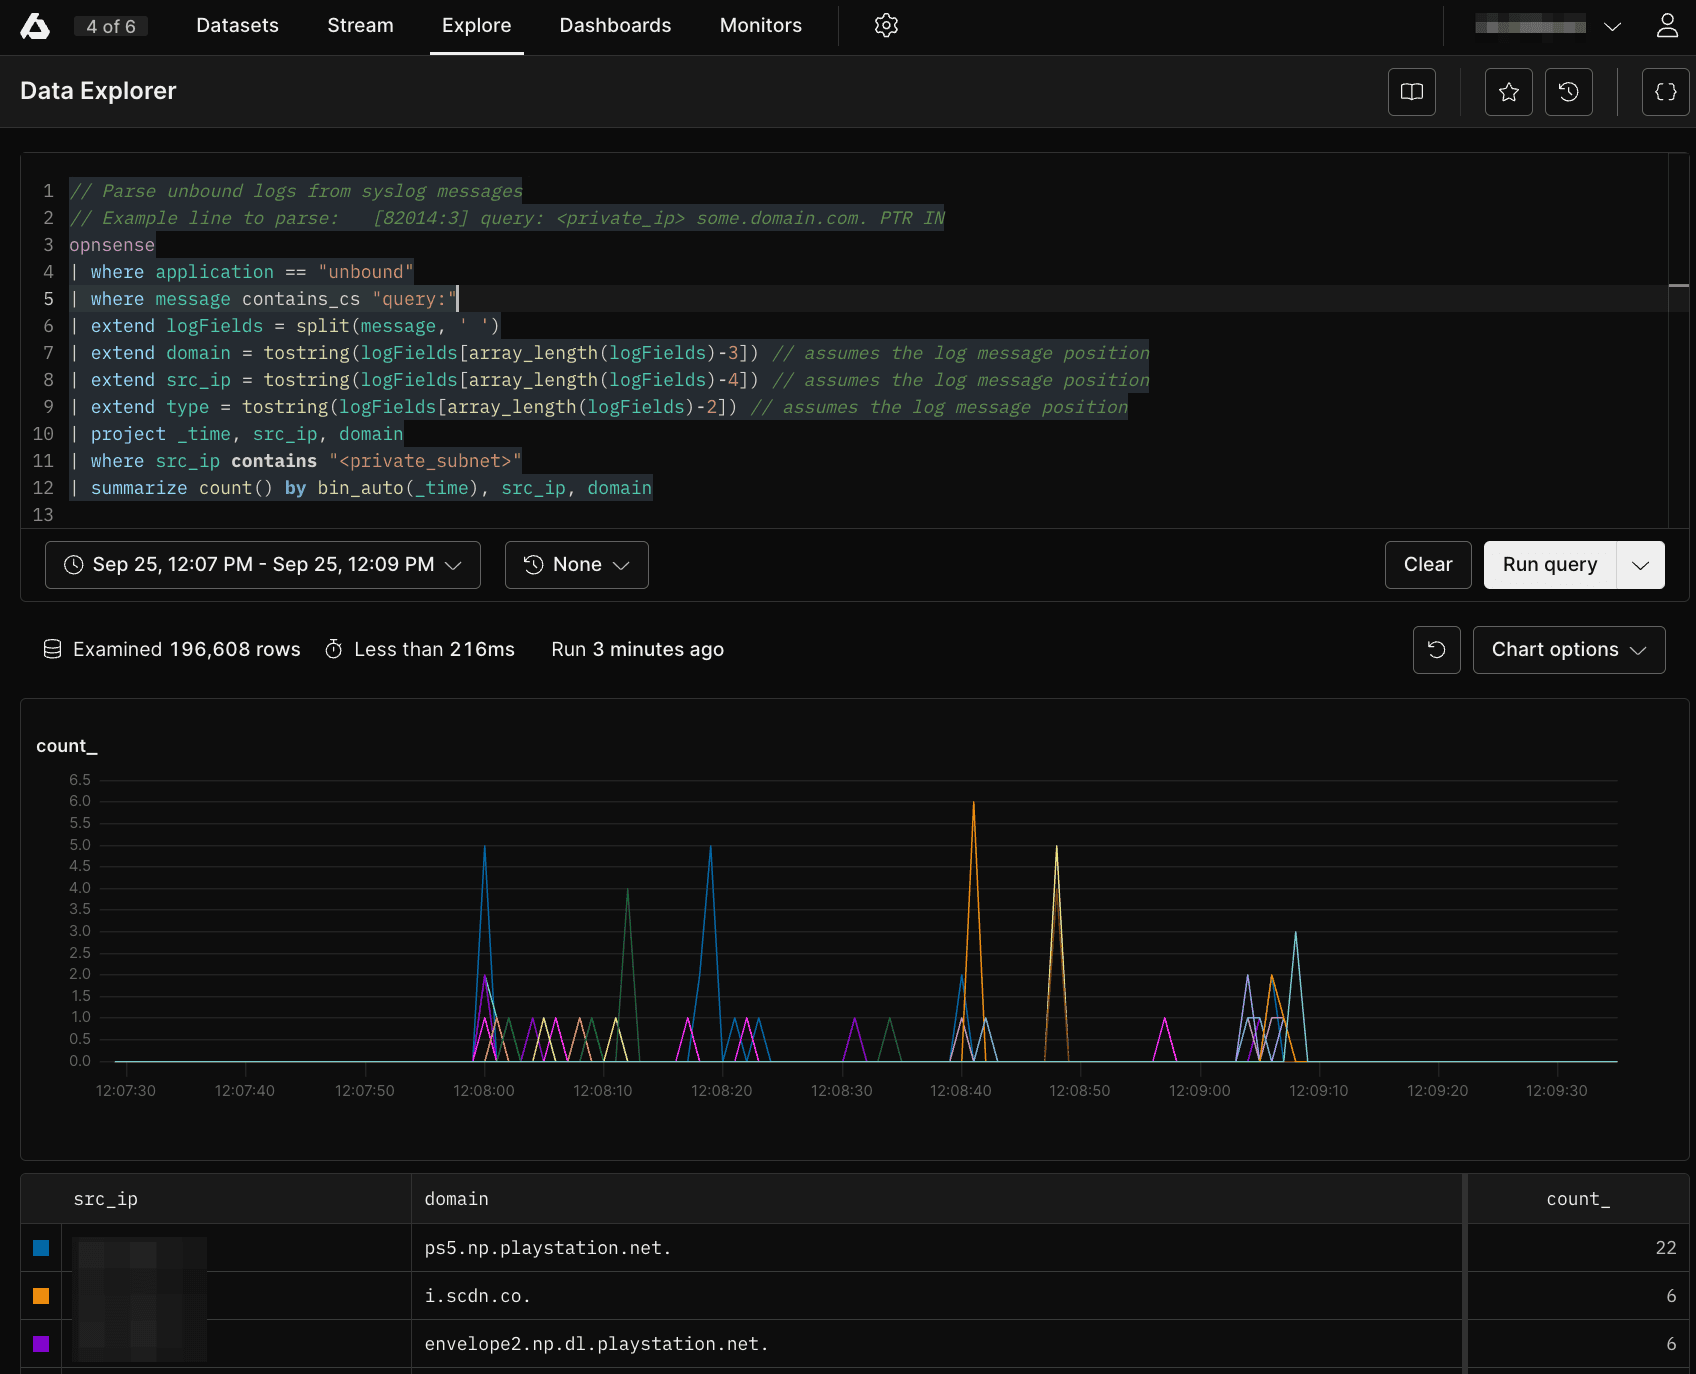
APL Query for the Above
Questions? Ideas? Talk to us at axiom.co/discord.